Establish a clear network boundary
Review internet lines, wired devices and the connections your business needs.

Integrated equipment. Accountable management. Ongoing protection.
Choose security equipment for your workplace, with named responsibility for configuration, updates and follow-up.
Review firewall rules, remote access and the connections your business needs.
Review network managementTrack managed computers, agreed endpoint protection and required updates.
See ongoing managementReview access, multi-factor authentication and account changes as staff join or leave.
Explore account protectionYou do not need a model number to start. Share your team size, locations and critical connections so we can discuss equipment, licences and management.
Review internet lines, wired devices and the connections your business needs.
Outline branch connections, remote access and who should reach each system.
Identify services that need continuity, then confirm compatibility and failover testing.
The agreed configuration and quotation identify the equipment model, available functions and support scope.
Discuss a scope that fits your business and budget. Confirm what is included and how it is charged before deciding.
HK$850/ month equivalent · from
Annual paymentHK$ 10,200 · Equipment rental + management
12 months paid annually in one payment. Monthly figures are equivalents only; monthly payment is not available.
1 rented firewall · 1 site · Agreed management
First standard on-site installation included · up to 4 hours
Unlimited remote requests and work hours for the contracted firewall
Within the selected plan’s agreed firewall-management scope and service hours
The starting plan is for one rented firewall. HA, additional equipment and compliance support are quoted separately.
Add Huorong Enterprise endpoint protection later as needed; licences are quoted separately.
Review the equipment, people and connections that need protection before choosing the scope.
Discuss the first priorities and later improvements around your available budget.
The proposal identifies equipment, licences, deployment and managed service charges, including one-off and recurring items.
People, locations, internet lines and services that matter.
Review equipment, licences, installation and ongoing management.
Set a change window, test connectivity and document responsibilities.

Try a failure. Compare one device with an active–standby pair.
Device B is ready, with health checks and synchronisation supported by the configuration.
Concept illustration: connections may be interrupted during takeover. Supported features, recovery time and failback must be tested for the configuration.
Plan for device failure before it happens. Assess whether active–standby deployment fits your critical connections, then agree testing and management responsibilities.
In a supported configuration, one device handles traffic while the standby checks its health and synchronises supported state. If a failure is confirmed, the standby can take over according to the agreed rules.
HA does not replace backups. Takeover may affect connections; compatibility, recovery time and failback need testing for the chosen deployment.
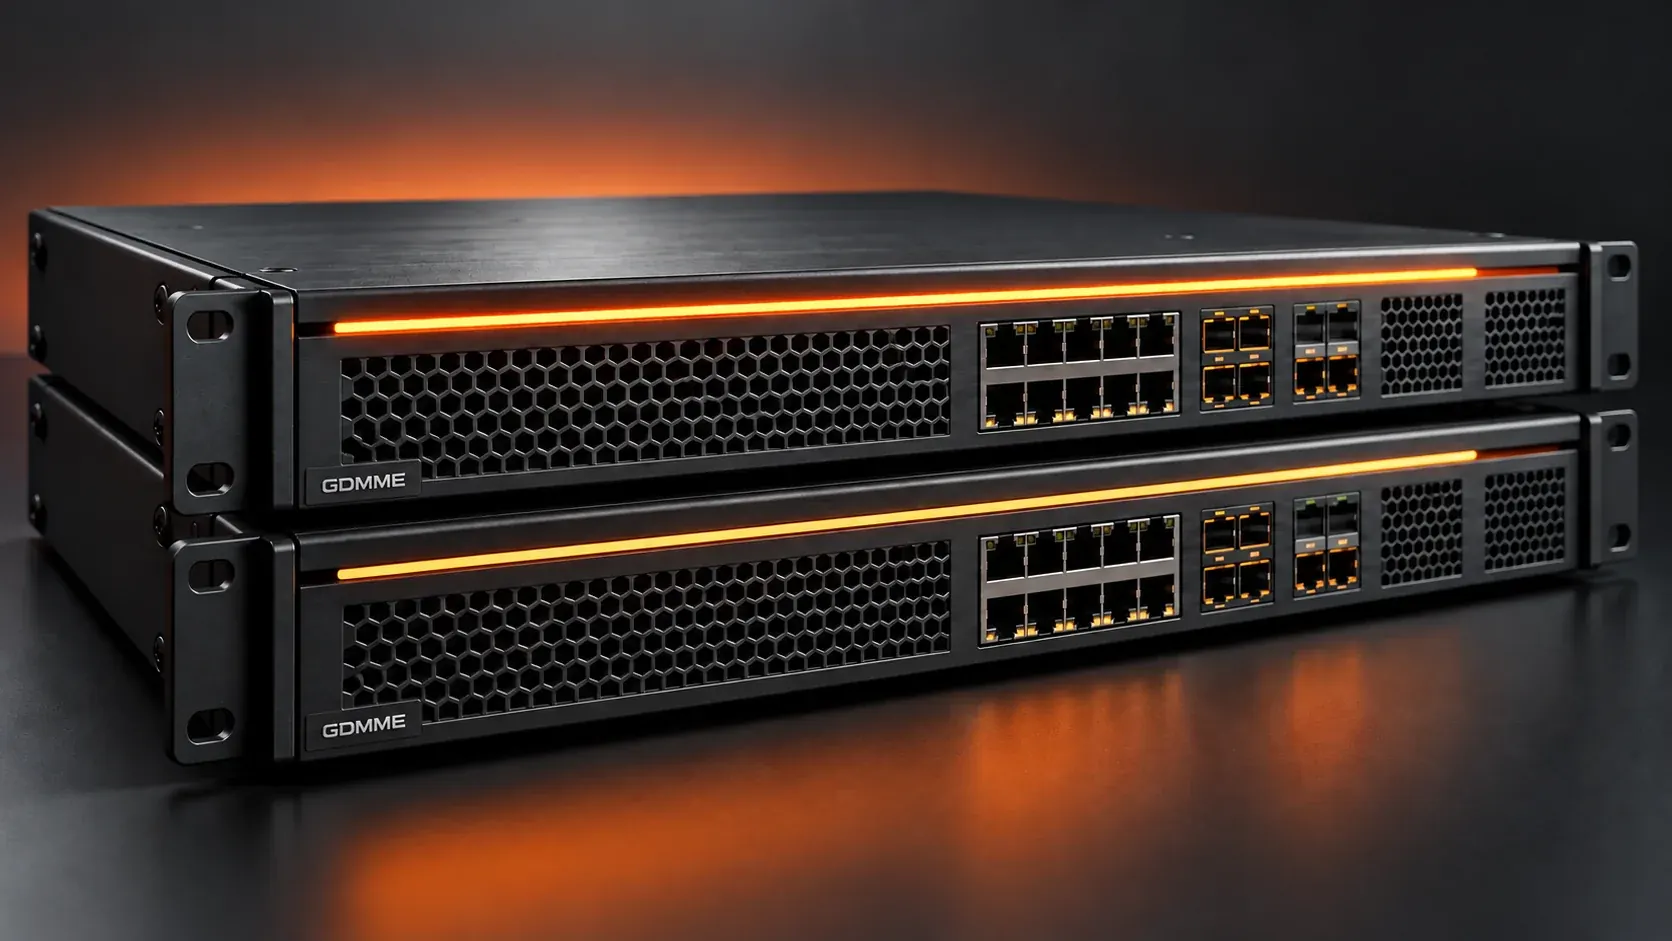
Explore the active–standby demonstrationChassis appearance is a development concept. The starting rental plan includes one firewall; HA and extra equipment are quoted separately. Final model, compatibility and management scope require confirmation.
Choose an industry to explore practical questions for your business.
 Equipment cabinet
Give the right people access to client files
Choose a topic to explore
Planning scenarios. Actual work and service hours are confirmed in the engagement scope.
Managed cybersecurity for Hong Kong businesses of different sizes. We agree what needs protecting, who is responsible and how the work will be reviewed.
Review and management of agreed firewalls, remote access and network segmentation.
Management of agreed endpoint protection, access controls and update schedules.
Review and escalation of relevant security alerts during contracted coverage hours.
Records of completed work, outstanding risks and priorities, including backup checks where contracted.
A baseline security review helps you understand current controls and prioritise practical improvements across your network, devices, accounts and recovery arrangements.
A record of systems, devices and responsible parties included in the review.
Review of agreed access permissions, multi-factor authentication, update status and remote access.
Examination of available backup records and recovery arrangements. Restoration testing is scoped separately.
Identified gaps, their business relevance and recommended next steps.
Start with three habits your team can practise in daily work.
Read the full sender address and domain. A familiar display name alone does not verify identity.
Confirm unusual payment or access requests using contact details you already know.
Do not send passwords or one-time codes to another person. Report unexpected sign-in prompts.
Pause the change. Call the supplier using previously verified contact details, then follow your internal approval process. Do not use a new number supplied in the suspicious message.
Your industry is already included. Submit here and keep your reference on this page.
Quote your reference when following up by email. Your email app opens only when you choose the button.
A supplier changes bank details. How do you check?
Choose a topic to explore
Planning scenarios. Actual work and service hours are confirmed in the engagement scope.
Managed cybersecurity for Hong Kong businesses of different sizes. We agree what needs protecting, who is responsible and how the work will be reviewed.
Review and management of agreed firewalls, remote access and network segmentation.
Management of agreed endpoint protection, access controls and update schedules.
Review and escalation of relevant security alerts during contracted coverage hours.
Records of completed work, outstanding risks and priorities, including backup checks where contracted.
A baseline security review helps you understand current controls and prioritise practical improvements across your network, devices, accounts and recovery arrangements.
A record of systems, devices and responsible parties included in the review.
Review of agreed access permissions, multi-factor authentication, update status and remote access.
Examination of available backup records and recovery arrangements. Restoration testing is scoped separately.
Identified gaps, their business relevance and recommended next steps.
Start with three habits your team can practise in daily work.
Read the full sender address and domain. A familiar display name alone does not verify identity.
Confirm unusual payment or access requests using contact details you already know.
Do not send passwords or one-time codes to another person. Report unexpected sign-in prompts.
Pause the change. Call the supplier using previously verified contact details, then follow your internal approval process. Do not use a new number supplied in the suspicious message.
Your industry is already included. Submit here and keep your reference on this page.
Quote your reference when following up by email. Your email app opens only when you choose the button.
Who can access what across your offices?
Choose a topic to explore
Planning scenarios. Actual work and service hours are confirmed in the engagement scope.
Managed cybersecurity for Hong Kong businesses of different sizes. We agree what needs protecting, who is responsible and how the work will be reviewed.
Review and management of agreed firewalls, remote access and network segmentation.
Management of agreed endpoint protection, access controls and update schedules.
Review and escalation of relevant security alerts during contracted coverage hours.
Records of completed work, outstanding risks and priorities, including backup checks where contracted.
A baseline security review helps you understand current controls and prioritise practical improvements across your network, devices, accounts and recovery arrangements.
A record of systems, devices and responsible parties included in the review.
Review of agreed access permissions, multi-factor authentication, update status and remote access.
Examination of available backup records and recovery arrangements. Restoration testing is scoped separately.
Identified gaps, their business relevance and recommended next steps.
Start with three habits your team can practise in daily work.
Read the full sender address and domain. A familiar display name alone does not verify identity.
Confirm unusual payment or access requests using contact details you already know.
Do not send passwords or one-time codes to another person. Report unexpected sign-in prompts.
Pause the change. Call the supplier using previously verified contact details, then follow your internal approval process. Do not use a new number supplied in the suspicious message.
Your industry is already included. Submit here and keep your reference on this page.
Quote your reference when following up by email. Your email app opens only when you choose the button.
How should maintenance fit production?
Choose a topic to explore
Planning scenarios. Actual work and service hours are confirmed in the engagement scope.
Managed cybersecurity for Hong Kong businesses of different sizes. We agree what needs protecting, who is responsible and how the work will be reviewed.
Review and management of agreed firewalls, remote access and network segmentation.
Management of agreed endpoint protection, access controls and update schedules.
Review and escalation of relevant security alerts during contracted coverage hours.
Records of completed work, outstanding risks and priorities, including backup checks where contracted.
A baseline security review helps you understand current controls and prioritise practical improvements across your network, devices, accounts and recovery arrangements.
A record of systems, devices and responsible parties included in the review.
Review of agreed access permissions, multi-factor authentication, update status and remote access.
Examination of available backup records and recovery arrangements. Restoration testing is scoped separately.
Identified gaps, their business relevance and recommended next steps.
Start with three habits your team can practise in daily work.
Read the full sender address and domain. A familiar display name alone does not verify identity.
Confirm unusual payment or access requests using contact details you already know.
Do not send passwords or one-time codes to another person. Report unexpected sign-in prompts.
Pause the change. Call the supplier using previously verified contact details, then follow your internal approval process. Do not use a new number supplied in the suspicious message.
Your industry is already included. Submit here and keep your reference on this page.
Quote your reference when following up by email. Your email app opens only when you choose the button.
Keep management consistent across locations
Choose a topic to explore
Planning scenarios. Actual work and service hours are confirmed in the engagement scope.
Managed cybersecurity for Hong Kong businesses of different sizes. We agree what needs protecting, who is responsible and how the work will be reviewed.
Review and management of agreed firewalls, remote access and network segmentation.
Management of agreed endpoint protection, access controls and update schedules.
Review and escalation of relevant security alerts during contracted coverage hours.
Records of completed work, outstanding risks and priorities, including backup checks where contracted.
A baseline security review helps you understand current controls and prioritise practical improvements across your network, devices, accounts and recovery arrangements.
A record of systems, devices and responsible parties included in the review.
Review of agreed access permissions, multi-factor authentication, update status and remote access.
Examination of available backup records and recovery arrangements. Restoration testing is scoped separately.
Identified gaps, their business relevance and recommended next steps.
Start with three habits your team can practise in daily work.
Read the full sender address and domain. A familiar display name alone does not verify identity.
Confirm unusual payment or access requests using contact details you already know.
Do not send passwords or one-time codes to another person. Report unexpected sign-in prompts.
Pause the change. Call the supplier using previously verified contact details, then follow your internal approval process. Do not use a new number supplied in the suspicious message.
Your industry is already included. Submit here and keep your reference on this page.
Quote your reference when following up by email. Your email app opens only when you choose the button.
Manage data and devices around patient care
Choose a topic to explore
Planning scenarios. Actual work and service hours are confirmed in the engagement scope.
Managed cybersecurity for Hong Kong businesses of different sizes. We agree what needs protecting, who is responsible and how the work will be reviewed.
Review and management of agreed firewalls, remote access and network segmentation.
Management of agreed endpoint protection, access controls and update schedules.
Review and escalation of relevant security alerts during contracted coverage hours.
Records of completed work, outstanding risks and priorities, including backup checks where contracted.
A baseline security review helps you understand current controls and prioritise practical improvements across your network, devices, accounts and recovery arrangements.
A record of systems, devices and responsible parties included in the review.
Review of agreed access permissions, multi-factor authentication, update status and remote access.
Examination of available backup records and recovery arrangements. Restoration testing is scoped separately.
Identified gaps, their business relevance and recommended next steps.
Start with three habits your team can practise in daily work.
Read the full sender address and domain. A familiar display name alone does not verify identity.
Confirm unusual payment or access requests using contact details you already know.
Do not send passwords or one-time codes to another person. Report unexpected sign-in prompts.
Pause the change. Call the supplier using previously verified contact details, then follow your internal approval process. Do not use a new number supplied in the suspicious message.
Your industry is already included. Submit here and keep your reference on this page.
Quote your reference when following up by email. Your email app opens only when you choose the button.
Separate teaching, administration and guest access
Choose a topic to explore
Planning scenarios. Actual work and service hours are confirmed in the engagement scope.
Managed cybersecurity for Hong Kong businesses of different sizes. We agree what needs protecting, who is responsible and how the work will be reviewed.
Review and management of agreed firewalls, remote access and network segmentation.
Management of agreed endpoint protection, access controls and update schedules.
Review and escalation of relevant security alerts during contracted coverage hours.
Records of completed work, outstanding risks and priorities, including backup checks where contracted.
A baseline security review helps you understand current controls and prioritise practical improvements across your network, devices, accounts and recovery arrangements.
A record of systems, devices and responsible parties included in the review.
Review of agreed access permissions, multi-factor authentication, update status and remote access.
Examination of available backup records and recovery arrangements. Restoration testing is scoped separately.
Identified gaps, their business relevance and recommended next steps.
Start with three habits your team can practise in daily work.
Read the full sender address and domain. A familiar display name alone does not verify identity.
Confirm unusual payment or access requests using contact details you already know.
Do not send passwords or one-time codes to another person. Report unexpected sign-in prompts.
Pause the change. Call the supplier using previously verified contact details, then follow your internal approval process. Do not use a new number supplied in the suspicious message.
Your industry is already included. Submit here and keep your reference on this page.
Quote your reference when following up by email. Your email app opens only when you choose the button.
Keep data access clear as roles change
Choose a topic to explore
Planning scenarios. Actual work and service hours are confirmed in the engagement scope.
Managed cybersecurity for Hong Kong businesses of different sizes. We agree what needs protecting, who is responsible and how the work will be reviewed.
Review and management of agreed firewalls, remote access and network segmentation.
Management of agreed endpoint protection, access controls and update schedules.
Review and escalation of relevant security alerts during contracted coverage hours.
Records of completed work, outstanding risks and priorities, including backup checks where contracted.
A baseline security review helps you understand current controls and prioritise practical improvements across your network, devices, accounts and recovery arrangements.
A record of systems, devices and responsible parties included in the review.
Review of agreed access permissions, multi-factor authentication, update status and remote access.
Examination of available backup records and recovery arrangements. Restoration testing is scoped separately.
Identified gaps, their business relevance and recommended next steps.
Start with three habits your team can practise in daily work.
Read the full sender address and domain. A familiar display name alone does not verify identity.
Confirm unusual payment or access requests using contact details you already know.
Do not send passwords or one-time codes to another person. Report unexpected sign-in prompts.
Pause the change. Call the supplier using previously verified contact details, then follow your internal approval process. Do not use a new number supplied in the suspicious message.
Your industry is already included. Submit here and keep your reference on this page.
Quote your reference when following up by email. Your email app opens only when you choose the button.
Network defence and high-availability planning for more resilient business connectivity
Switch equipment on and off to explore network protection and resilience
Landscape fullscreen Fits your screen with zoom for detail
This simulation uses landscape fullscreen Enable auto-rotate The diagram will fit your screen
Hover over the diagram and press Alt + Enter for full screen
App and database HA assume configured failover · Backup does not automatically take over · Recovery points and times are not simulated · Fans and cooling are concepts Environmental monitoring is not connected
UPS A/B feed separate PDUs and dual PSUs · Upstream independence requires site verification
Port names and VLANs are planning examples not deployed settings Verify interfaces modules power and compatibility against the selected equipment
The 3F Huorong control center is a separate management server Teal dashes show logical policy and status traffic over the existing LAN rather than dedicated cables This example retains endpoint protection when the center is unavailable Verify actual version and deployment behavior
| # | From → To | Cable / interface | Plan & verification |
|---|---|---|---|
| 01 | ISP 1 / ISP 3 → ISP Switch A | RJ45 / CAT6 | Separate WAN VLANs 101 / 103 Keep provider broadcast domains isolated |
| 02 | ISP 2 / 4G・5G → ISP Switch B | RJ45 / CAT6 | Separate VLANs 102 / 104 Cellular is a backup path |
| 03 | ISP Switch A ↔ B | 802.1Q TRUNK | Permit planned WAN VLANs only Configure loop prevention |
| 04 | ISP Switch A / B → HA A + HA B | WAN-A / WAN-B | Both HA members connect to both WAN switches through separate interfaces |
| 05 | HA A ↔ HA B | HA1 + HA2 | Two dedicated heartbeat cables are proposed Shown as one grouped route Separate from WAN |
| 06 | HA A + HA B → Core A / B | LAN-A / LAN-B | Use a supported stack MLAG or routed design Do not treat independent switches as a single LACP peer |
| 07 | Core A ↔ Core B | PEER / ISL | Plan peer and keepalive links according to the selected platform Shown grouped |
| 08 | Core A / B → ODF → 1F 2F 4F 5F 6F 7F | FIBER A + B | Two uplinks per floor via fibre patching Match transceivers fibre type and distance |
| 09 | Floor Switch → Patch Panel → AP | CAT6 / PoE | Copper via patch panels and cable managers to APs Verify PoE standard and power budget |
| 10 | Core A / B → AC A + AC B | LAN / AC HA | Both HA controllers connect to both cores Requires compatible HA and configuration sync The 3F AP uses Core A with PoE provision to be verified |
| 11 | UPS A → PDU A / UPS B → PDU B | POWER A + B | Dual PSUs use separate A/B PDUs Either path can supply power Do not directly parallel UPS outputs Verify upstream circuit independence and capacity |
Racks include app A/B database A/B and a separate backup server Service HA assumes compatible failover and replication Backup connectivity does not prove valid backups Verify offline or immutable copies and restore tests Huorong shields illustrate assumed deployment rather than real installation status
Department VLANs still need inter-zone access policy Microsegmentation can apply policy per host or workload Implementation needs a supported host firewall agent or network platform VLANs and microsegmentation are not simulated here
Technical references Follow the selected platform No partnership with these vendors is implied ·HA Heartbeat ·VSF / VSX ·Huorong enterprise ·WebRAY RayScan
From deployment to daily management, give administrators a clear entry point and agree configuration and access by authorisation.
Interface previewDisplay only · No account details required
 FIREWALL
See your network clearly, shape its policies and control access by authorisation.
 NETWORK · POLICY · ACCESS
Use your assigned account to continue.
Account assistance: Contact your administrator.This illustrates the sign-in design without connecting to a device or collecting sign-in details. The actual interface and features depend on the device version and deployment.
Discuss equipment and management →Start with a review, ongoing management or a support enquiry.
For businesses that need ongoing security management, a review of current IT support, or clearer ownership of security work.
Explore managed securityFor businesses planning an IT handover, checking current protection, or starting a structured review of security responsibilities.
See what we reviewFor businesses seeking a practical assessment of support and recovery options following a suspected security incident.
Understand incident supportGood equipment needs consistent management. Keepchecks, responsibilities and next actions visible, so you know how security work is progressing.
Explore management and handoverChoose what matters to your business and explore GDMME.
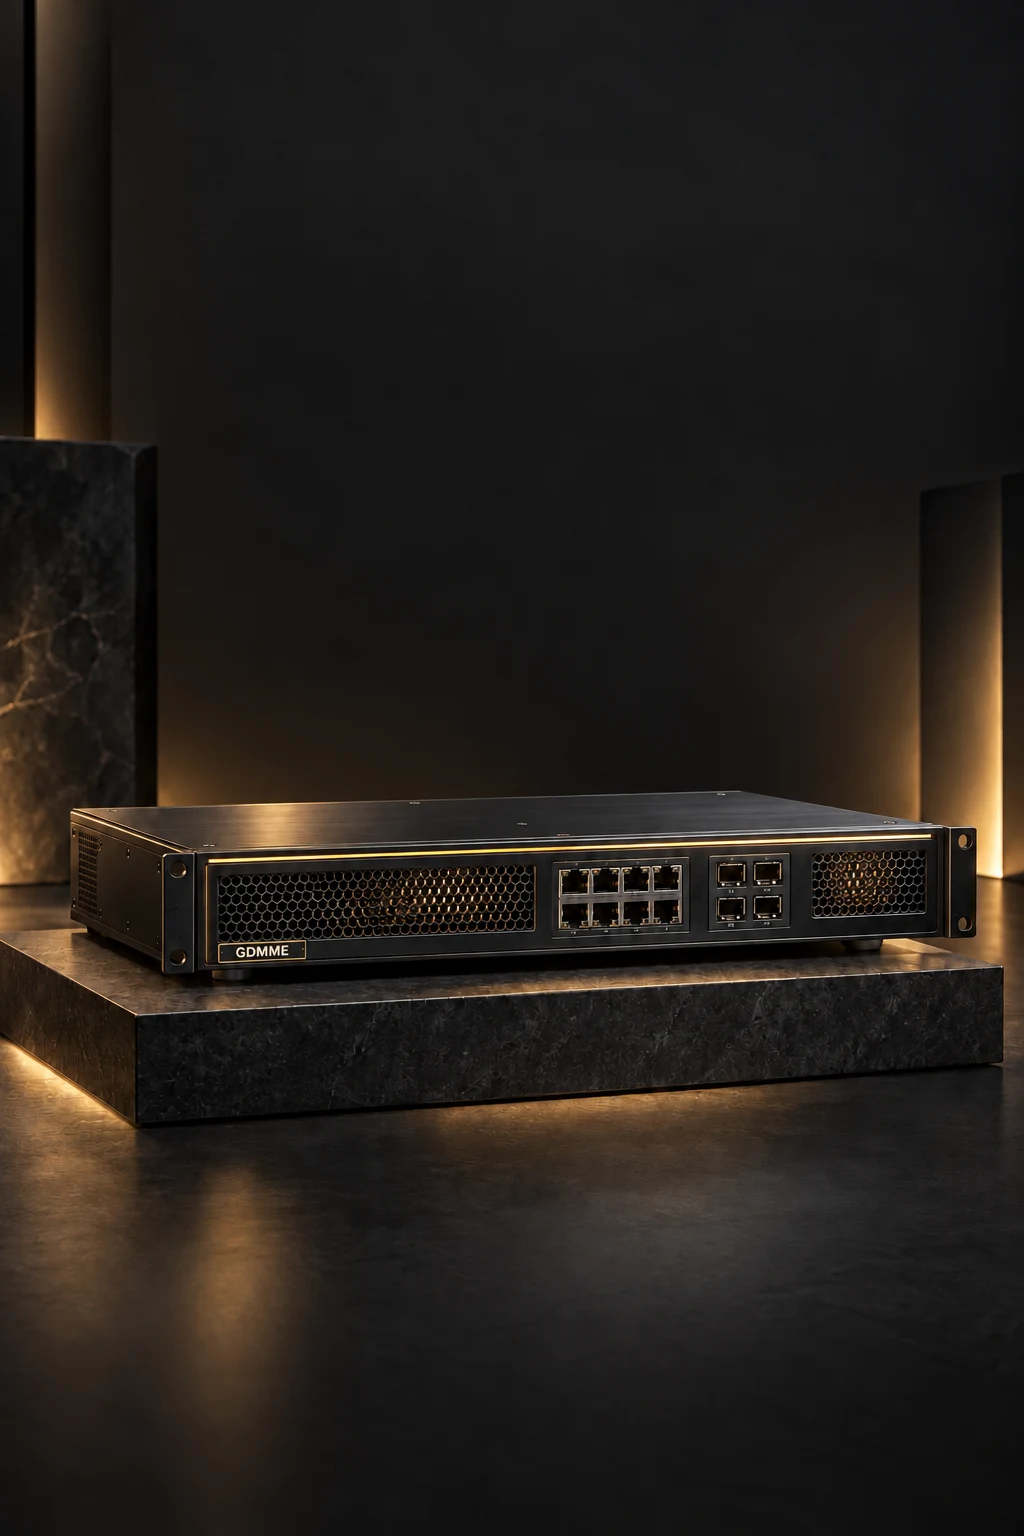
Equipment and network boundaries planned around your business
Update checks · Access reviews · Follow-up records
Start with phishing emails and identity checks
In the age of AI-enabled scams, encryption is only part of the picture. Know who you are dealing with.
Your company normally uses harbour.example. Select the three highlighted areas to see what deserves a closer look.
Try the full practice libraryRansomware initial checkView global cyber threat intelligenceFrom: IT Support
0 of 3 clues explored
Select a highlighted area to read the explanation.
The sender’s domain differs from harbour.example. A familiar display name can be copied; verify using a contact you already know.
Genuine messages can also be urgent. Use a known telephone number or independently open the official service to check.
A verification code may authorise sign-in or an action. Do not send it to someone by email.
Explore the clues, then practise with a full scenario.
Continue to full practiceTell us your company size and what you want to improve.